1. The Technology That Could Change Cybersecurity Forever For decades, the security of the digital economy has depended on mathematical problems that are extremely difficult for conventional computers to solve. These systems help protect online banking, secure communications, digital identities and cryptocurrency transactions.
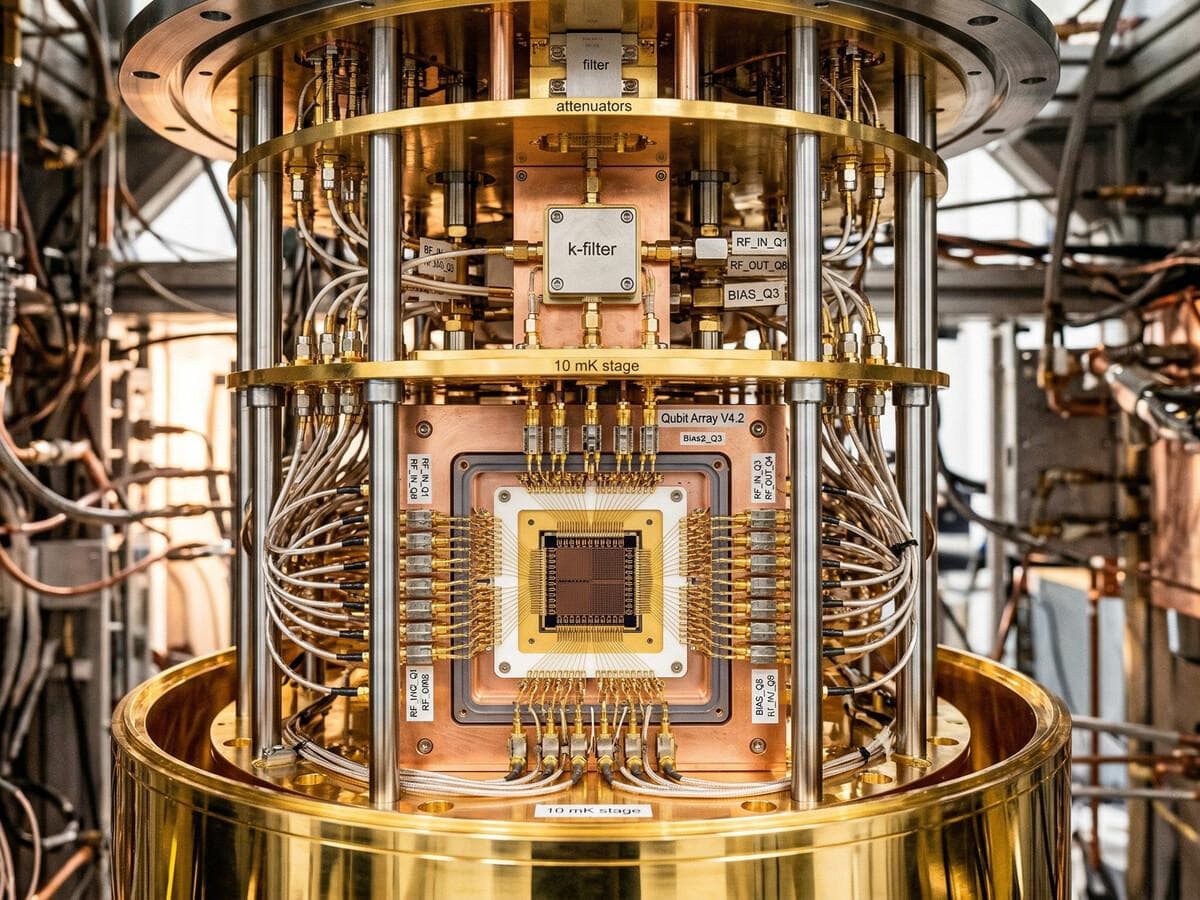
Quantum computing introduces a different way of processing information. Rather than simply making ordinary computers faster, quantum computers use quantum-mechanical effects to solve certain specialised problems in fundamentally different ways.
That distinction matters because sufficiently powerful quantum computers could solve some mathematical problems that underpin widely used public-key cryptography. Algorithms such as RSA and elliptic-curve cryptography are used across digital infrastructure to help establish secure connections and verify identities.
If a large, fault-tolerant quantum computer becomes capable of running the necessary algorithms at scale, it could threaten systems that are considered secure against today's conventional computers.
The US National Institute of Standards and Technology (NIST) has warned that organisations should begin moving towards post-quantum cryptography rather than waiting for the threat to materialise. It has already finalised standards designed to protect information against future quantum attacks. [1]
This does not mean quantum computers can currently break global banking encryption at will. Building a machine capable of doing so remains a major technical challenge.
The concern is that replacing cryptography across the global economy could take years, making preparation necessary well before the technology reaches that point. 2. How Quantum Computers Could Break Today's Encryption Much of modern cybersecurity relies on two broad cryptographic functions: encryption and digital signatures.
Encryption helps keep information confidential, so that only authorised parties can read it. Digital signatures help establish authenticity, allowing systems to verify that a message, transaction or software update genuinely came from the expected source.
Quantum computers threaten these functions in different ways.
Shor's algorithm, a quantum algorithm developed in the 1990s, could theoretically solve the mathematical problems behind RSA and elliptic-curve cryptography efficiently if executed on a sufficiently capable, fault-tolerant quantum computer. These systems are widely used for public-key encryption, key establishment and digital signatures.
Grover's algorithm presents a different, more limited threat to certain symmetric-key cryptographic systems. It can offer a quadratic speed-up for searching possible keys, rather than the dramatic effect Shor's algorithm has on certain public-key systems. Appropriate key sizes can help mitigate this risk.
The distinction is important. Quantum computing would not automatically make every form of encryption useless. Some cryptographic methods can be strengthened, while others can be replaced with algorithms designed to resist quantum attacks.
The immediate challenge is identifying which systems are vulnerable, selecting appropriate replacements and ensuring those replacements work reliably across interconnected networks. 3. The Global Banking System Is Preparing for the Threat Banks rely on cryptography throughout their operations, from customer logins and secure communications to payment infrastructure and the management of sensitive financial data.
A future quantum attack could threaten vulnerable systems that establish secure connections or verify digital identities. Depending on the system and circumstances, attackers might be able to impersonate legitimate parties, compromise protected communications or forge digital signatures.
That would have implications beyond individual bank accounts. Financial institutions depend on networks of technology suppliers, payment providers, software platforms and other banks. A weakness in one part of that ecosystem could create risks for connected organisations.
In January 2026, the G7 Cyber Expert Group, co-chaired by the US Treasury and the Bank of England, published a roadmap outlining considerations for financial institutions, regulators and suppliers preparing for the transition to quantum-resilient technology. The statement emphasised the need for coordinated and timely action. [2]
The roadmap reflects a key reality: banks cannot treat quantum readiness as a problem for their cybersecurity departments alone.
They must understand where vulnerable cryptography is used, which suppliers support critical services, how long upgrades will take and how to maintain operations during the transition.
The financial sector also faces a coordination problem. A bank may upgrade its own systems but remain dependent on a payment processor, software provider or legacy platform that has not completed its migration.
Quantum resilience will therefore require cooperation across the wider financial ecosystem. 4. Could Quantum Computers Really Crack Bitcoin? Bitcoin is among the most frequently discussed potential targets because its security relies partly on elliptic-curve cryptography.
Bitcoin transactions use digital signatures to demonstrate that someone has the authority to spend funds associated with a particular key. If a sufficiently powerful quantum computer could derive a private key from its corresponding public key, it could potentially allow an attacker to spend the associated funds.
That would represent a serious challenge for a system built around cryptographic ownership.
However, the risk is more nuanced than headlines suggesting that every Bitcoin wallet could be emptied overnight.
Bitcoin uses different cryptographic mechanisms for different purposes. Its proof-of-work mining system relies on hashing, while transaction authorisation relies on digital signatures. Quantum attacks would affect these mechanisms differently.
The most direct concern is the potential compromise of vulnerable digital signatures. The exposure of a particular wallet depends on its address type, whether its public key has been revealed, how funds are stored and the capabilities of the attacking quantum computer.
Some Bitcoin public keys become visible when funds are spent. Other address formats can conceal the public key until a spending transaction reveals it. These differences affect the potential window of vulnerability.
In July 2026, Reuters reported growing concern within the cryptocurrency industry about the quantum threat, including research suggesting that the timeline for preparing could be shorter than previously assumed. The report also described efforts by crypto companies to investigate possible defences. [3]
Such reporting should not be interpreted as evidence that a machine capable of stealing Bitcoin at scale already exists.
The practical threat depends on the capabilities of future quantum hardware, the cryptographic implementation and whether the Bitcoin network can coordinate and deploy suitable changes in time. 5. What About XRP and Other Cryptocurrencies? Bitcoin is not the only digital asset whose security depends on public-key cryptography.
Many blockchain networks use elliptic-curve signatures or related cryptographic systems to authorise transactions. If those systems are vulnerable to a sufficiently powerful quantum computer, their networks could face similar questions about wallet security and migration.
The details differ between blockchains. Each network has its own signature schemes, address formats, upgrade mechanisms and governance arrangements. It would therefore be inaccurate to assume that every cryptocurrency has precisely the same level of exposure.
For XRP, for example, the relevant issue is the cryptographic system used to authorise transactions and how the XRP Ledger could respond if those systems became vulnerable. Any transition would need to account for network compatibility, wallet software, exchanges, custody providers and the practical handling of existing accounts.
The same general challenge applies to other networks: quantum resistance cannot be achieved simply by announcing that a blockchain is secure. The underlying cryptography must be evaluated, changes must be implemented correctly, and users must have a workable route to protect their assets.
Investors should also be cautious about projects marketing themselves as quantum-proof without providing credible technical evidence or independent security assessments.
A cryptocurrency's exposure to quantum risk is only one element of its overall risk profile. Market volatility, liquidity, custody, regulation and ordinary software vulnerabilities remain important regardless of advances in quantum computing. 6. The Hidden Risk: Stolen Data That Could Be Decrypted Later One of the most concerning aspects of the quantum threat is the possibility of a “harvest now, decrypt later” attack.
In this scenario, an attacker collects encrypted information today, even though they cannot currently read it. The attacker stores that data and waits in the hope that future technology will make it possible to decrypt.
This matters when the information remains valuable or sensitive for many years.
Examples include confidential business plans, government communications, intellectual property, medical records and sensitive financial information. The exact exposure depends on the cryptographic system used and the attacker's ability to obtain the encrypted data.
Not all encrypted information is equally vulnerable, and a future quantum computer would not automatically decrypt every captured file. However, organisations handling long-lived secrets need to consider whether information stolen today could still cause harm if exposed in the future.
This changes the way businesses must think about cybersecurity timelines.
If a company needs to protect information for the next 15 or 20 years, it cannot base its decisions solely on whether quantum computers pose an immediate threat. It must also consider how long migration will take and how valuable the information may remain.
Waiting until quantum attacks become practical could leave too little time to protect data that was collected years earlier. 7. The Solution: Post-Quantum Cryptography The main defence being developed is post-quantum cryptography, often abbreviated as PQC.
PQC uses mathematical approaches intended to resist attacks from both conventional and quantum computers. Unlike quantum cryptography, it does not require organisations to replace ordinary computers with quantum machines. Instead, it involves deploying new cryptographic algorithms on conventional hardware and within existing digital systems.
In August 2024, NIST finalised three important standards:
• FIPS 203 — ML-KEM: A mechanism for establishing shared secret keys over potentially insecure communications.
• FIPS 204 — ML-DSA: A digital-signature standard designed to resist quantum attacks.
• FIPS 205 — SLH-DSA: Another digital-signature standard based on hash functions. These standards provide a foundation for replacing vulnerable cryptographic methods in a wide range of applications. NIST has encouraged organisations to begin implementing the new standards rather than waiting for quantum computers to become a practical threat. [1]
However, standardising algorithms is only the beginning.
Software, network protocols, hardware security modules, identity systems and other components must be updated and tested. Organisations also need to ensure that new implementations are secure and compatible with the services they depend on.
PQC is not a single software update that can instantly protect the entire internet. It is a large-scale technology transition that will involve many systems and suppliers. 8. The UK's 2035 Deadline The UK is already planning for a future in which quantum-resistant cryptography becomes the norm.
In March 2025, the National Cyber Security Centre (NCSC) published guidance setting out three key milestones for organisations migrating to post-quantum cryptography. [4]
2028 — Identify and plan: Organisations should assess where vulnerable cryptography is used, identify dependencies and establish a migration plan.
2031 — Prioritise critical systems: High-priority migration work should be completed, with plans refined to cover the remaining systems.
2035 — Complete the transition: The NCSC's target is for organisations to complete migration of their systems, services and products to post-quantum cryptography.
These dates are migration targets, not predictions that a quantum computer will break banking security in 2028, 2031 or 2035.
The schedule reflects the scale of the work involved. Large organisations may spend years discovering where cryptography is used, coordinating with suppliers, replacing older systems and testing new implementations.
For smaller businesses that mainly use standard commercial software, much of the transition may arrive through routine updates from their technology providers. Organisations running bespoke systems or critical infrastructure may face a more complicated process.
The message from the UK's cybersecurity agency is clear: preparation needs to begin before the threat becomes urgent. 9. Why Upgrading the World's Security Is So Difficult Replacing cryptography across global digital infrastructure is not comparable to updating a single application.
Large organisations may rely on thousands of systems, including older software, specialist hardware and third-party services. Some equipment may be difficult to replace, while some software may no longer be actively maintained.
A cryptographic upgrade can also create compatibility problems. Two systems need to agree on how to establish secure communications, authenticate one another and handle cryptographic keys. If one system supports new algorithms and another does not, the connection may fail or fall back to a less secure option.
Businesses must also guard against implementation mistakes. A mathematically sound algorithm can still be deployed incorrectly, undermining the protection it is intended to provide.
Another challenge is cost. Organisations will need technical expertise, testing, procurement, software development and potentially new hardware. The cost will vary substantially depending on the size and complexity of each organisation's technology estate.
For financial institutions, the transition must be carefully coordinated to avoid disrupting payments, customer services or essential operations.
This is why quantum readiness is increasingly a question of operational resilience and long-term investment, not just cryptographic research. 10. Could the Quantum Threat Trigger a Crypto Market Shock? The prospect of quantum attacks could influence investor sentiment long before the technology becomes capable of breaking blockchain security.
If investors become concerned that a cryptocurrency's underlying cryptography is vulnerable, they may question whether its developers can coordinate a safe upgrade. Uncertainty around dormant wallets, exposed public keys and the migration of existing holdings could also create controversy.
However, the impact on market prices is difficult to predict. A credible migration plan could reduce concern, while a major breakthrough in quantum computing or evidence of a practical cryptographic attack could increase it.
The response would also differ between networks. Some may be better positioned to introduce changes, while others could face disagreements over protocol upgrades, backward compatibility or how to handle assets that cannot be migrated easily.
Investors should distinguish between a genuine technical development and promotional claims designed to create fear or sell a supposedly quantum-resistant token.
A project claiming to solve the quantum problem should be evaluated on the strength of its cryptography, independent reviews, implementation quality and adoption — not on the word “quantum” in its marketing.
For cryptocurrency holders, the sensible approach is to follow credible technical guidance and network-specific announcements rather than panic-selling in response to speculative headlines. 11. The Investment Opportunity in Quantum Security The need to modernise cryptography could create opportunities for businesses providing cybersecurity software, secure hardware, cryptographic management and migration services.
Financial institutions and large enterprises will need to identify vulnerable systems, evaluate replacement algorithms, coordinate upgrades and verify that their new infrastructure works correctly.
That could support demand for specialist security consultancies, software providers and hardware manufacturers. Cloud providers and enterprise technology companies may also benefit as quantum-resistant features become part of standard products and services.
However, the opportunity should not be mistaken for a guaranteed investment return.
The transition will take years, and much of the work may be incorporated into existing cybersecurity products rather than generating a separate, high-growth revenue stream. Competition could also put pressure on prices.
Investors should examine whether companies have established customers, credible technical expertise, measurable demand and a sustainable business model.
There is a further distinction between companies building quantum computers and companies protecting systems against them. Both are part of the wider quantum technology ecosystem, but their commercial opportunities and risks are very different.
The most attractive businesses may ultimately be those that help organisations manage the transition reliably, rather than those making the boldest claims about when quantum computers will arrive. 12. Is the World Running Out of Time? There is no universally agreed date for when a quantum computer capable of breaking widely used public-key cryptography will become practical.
Progress depends on difficult engineering problems, including scaling quantum hardware, reducing errors and building reliable fault-tolerant systems. Estimates can change as researchers make advances, but a specific forecast should not be treated as a guaranteed deadline.
The absence of a firm date is precisely why cybersecurity authorities are recommending action now.
The NCSC's migration roadmap recognises that the transition is a multi-year process and sets 2035 as the target for completing migration. [4] The G7's financial-sector work also reflects the need for coordinated preparation across institutions and suppliers. [2]
Waiting for certainty would be a risky strategy. If a breakthrough arrives sooner than expected, organisations that have not mapped their cryptographic dependencies may struggle to upgrade in time.
At the same time, fear-driven claims that Bitcoin or banking systems are about to collapse are not supported by the current state of quantum computing.
The realistic position lies between complacency and panic: the threat is not an immediate universal collapse, but it is significant enough to justify sustained preparation. Conclusion: The Quantum Threat Is a Race Against Time Quantum computing could eventually challenge some of the cryptographic foundations that protect the global economy. Banking, digital identity systems, encrypted communications and cryptocurrencies may all need to adapt as the technology advances.
But the outcome is not predetermined.
Post-quantum cryptography standards already exist, and governments and financial institutions are working towards migration. The challenge is to deploy those protections correctly, coordinate upgrades across complex supply chains and ensure that vulnerable systems are not left behind.
For Bitcoin and other cryptocurrencies, the issue is particularly important because network upgrades must account for digital signatures, existing wallets, users and decentralised governance. The risk should be taken seriously, but it should not be confused with proof that current wallets can already be cracked by quantum computers.
The same principle applies to banking: the need to prepare does not mean today's systems have suddenly become insecure.
The real quantum computing time bomb is not a known date when every encryption system will fail. It is the possibility that the technology advances faster than the world can replace the systems it depends on.
The organisations that begin preparing early will have more time to test, adapt and protect their users. Those that wait for an unmistakable warning may discover that securing the digital economy is a much larger task than they anticipated. Sources [1] US National Institute of Standards and Technology (NIST) — Post-Quantum Cryptography https://www.nist.gov/pqc
[2] US Department of the Treasury — G7 Cyber Expert Group Releases Roadmap for Coordinating the Transition to Post-Quantum Cryptography in the Financial Sector (12 January 2026) https://home.treasury.gov/news/press-releases/sb0355
[3] Reuters — Crypto firms prepare defenses as quantum threat to encryption draws nearer (8 July 2026) https://www.reuters.com/legal/government/crypto-firms-prepare-defenses-quantum-threat-encryption-draws-nearer-2026-07-08/
[4] UK National Cyber Security Centre (NCSC) — Timelines for migration to post-quantum cryptography (20 March 2025) https://www.ncsc.gov.uk/guidance/pqc-migration-timelines
[5] NIST — Announcing Approval of Three Federal Information Processing Standards (FIPS) for Post-Quantum Cryptography (13 August 2024) https://www.nist.gov/news-events/news/2024/08/announcing-approval-three-federal-information-processing-standards-fips
Published by Banx Network. This article is part of the Banx decentralized media programme, powered by the BXE token on the XRP Ledger.